Counting the Real Cost of a Disposal-Related Data Incident
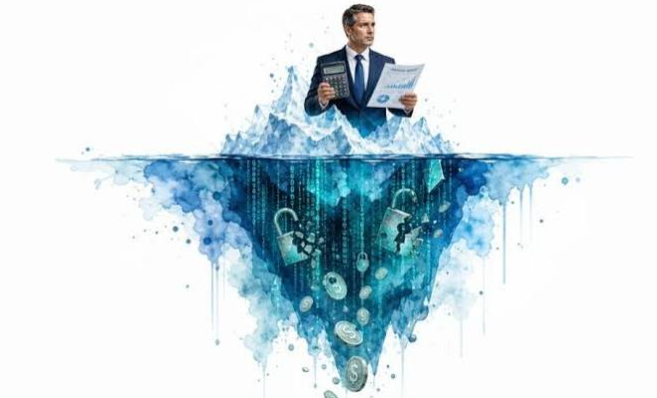
Security budgets get allocated to the threats people can picture. Phishing, ransomware, credential theft, and network intrusion all have vivid narratives attached, and they attract attention accordingly. A drive that left the building in a box and was never properly destroyed has no narrative at all, which is why it tends to sit at the bottom of the priority list.
That ranking does not survive contact with the actual numbers. Incidents originating from improperly disposed media are less frequent than phishing incidents, but they share characteristics that make them disproportionately expensive when they occur: the exposure is often complete rather than partial, the timeline is unknown, and the organization usually cannot say what was on the media.
Which is why the comparison worth making is not between the cost of ssd destruction services and the cost of doing nothing, but between that cost and the cost of the specific failure it prevents. Once the second number is estimated honestly, the first stops looking like an expense.
Why the Unknown Scope Drives the Cost
In a typical network intrusion, forensic investigation can usually establish what was accessed and when. Logs exist, systems retain evidence, and the scope of the incident can be bounded.
A drive that went missing during disposal offers none of that. There are no logs. There is no timeline. There is frequently no record of what the machine held, because it was decommissioned before anyone catalogued its contents.
The regulatory consequence of that uncertainty is significant. When an organization cannot demonstrate which records were on the media, notification obligations generally extend to everyone who could plausibly have been affected. A single drive from a finance workstation can therefore trigger notification to a customer base rather than to a handful of individuals.
That expansion of scope is what drives the cost, and it flows directly from the absence of records rather than from the severity of the exposure itself.
The Cost Components That Actually Add Up
Notification itself is a direct expense, involving identification of affected individuals, drafting, mailing, and a call centre to handle responses. At scale it becomes substantial before any penalty is considered.
Credit monitoring is customary where financial or identity information is involved, priced per person per year, and it is difficult to decline once it has become the norm.
Forensic and legal costs accrue regardless of outcome. Establishing what happened, advising on obligations across jurisdictions, and managing the regulator relationship all consume specialist time.
Regulatory penalties vary widely by jurisdiction and by conduct. What is consistent across frameworks is that penalties are influenced heavily by whether the organization had reasonable controls in place. An organization with a documented disposal process that failed once is treated very differently from one that had no process at all.
Business disruption is the component people forget. Senior staff time consumed by incident management is real cost, and it lands on the people the organization can least afford to divert.
Then there is the commercial impact: contract terms with enterprise customers that require notification, procurement questionnaires that will ask about the incident for years, and the effect on renewal conversations.
Why the Preventive Cost Is So Small By Comparison
The asymmetry here is unusually stark. Destroying storage media properly costs a modest amount per drive, and even a large organization retiring thousands of drives annually is looking at a figure that rounds to nothing against the cost components above.
The surrounding controls cost even less. An inventory record at removal is a spreadsheet entry. A locked cabinet is a one-time purchase. A scheduled collection replaces an ad hoc one at similar cost. Reconciling a certificate takes minutes.
What these controls buy is not only prevention but defensibility. An organization that can produce serial-level destruction records for its retired media is in a fundamentally different position during an investigation than one that can produce a policy document and a general assurance.
The Failure Points Worth Spending On
If the budget is limited, the spending should follow where incidents actually originate.
The storage gap is first. Media sitting between decommissioning and processing, in an unlocked room accessible to many people, is where drives most often disappear. A locked container and a short processing interval address the largest single exposure at almost no cost.
Inventory is second. Without a record of what was removed, no discrepancy can ever be detected, which means a missing drive is discovered only when it surfaces somewhere else.
Verification is third. Solid state media does not respond reliably to conventional overwriting, so an organization relying on software erasure for flash storage may have an exposure it believes it has closed. Destruction removes that uncertainty.
Documentation is fourth, and it is what converts the other three into evidence.
Framing It for a Budget Conversation
The argument that works is not the environmental one and it is not the compliance one, though both are true. It is the exposure calculation.
Estimate the number of drives leaving the organization annually. Estimate the record count a typical drive from a sensitive role might hold. Apply a defensible per-record incident cost from published industry figures. Compare that to the annual cost of proper destruction and the surrounding controls.
The ratio is usually wide enough that the conversation ends quickly, which is generally the point at which a process that everyone agreed was sensible finally gets funded.